Polosukhin’s assessment focuses on the fragility of modern web stacks, where a single compromised component often destabilizes entire downstream applications. He specifically highlighted risks within PHP-based environments like WordPress, alongside vulnerabilities in TLS certificate handling and LiteLLM packages. These technical flaws, ranging from memory-handling errors to improper credential routing, create a compounding effect that exposes the broader internet to coordinated threats.
In section Cryptocurrency
NEAR Co-Founder Warns of Pervasive 'Security Armageddon'
“We are at Security Armageddon now,” declares Illia Polosukhin, co-founder of NEAR Protocol, pointing to a cascading crisis of software vulnerabilities. He warns that deep-seated weaknesses in aging internet infrastructure—from PHP systems to Node.js—are creating a wide-open landscape for attackers to exploit interconnected services across the digital ecosystem.
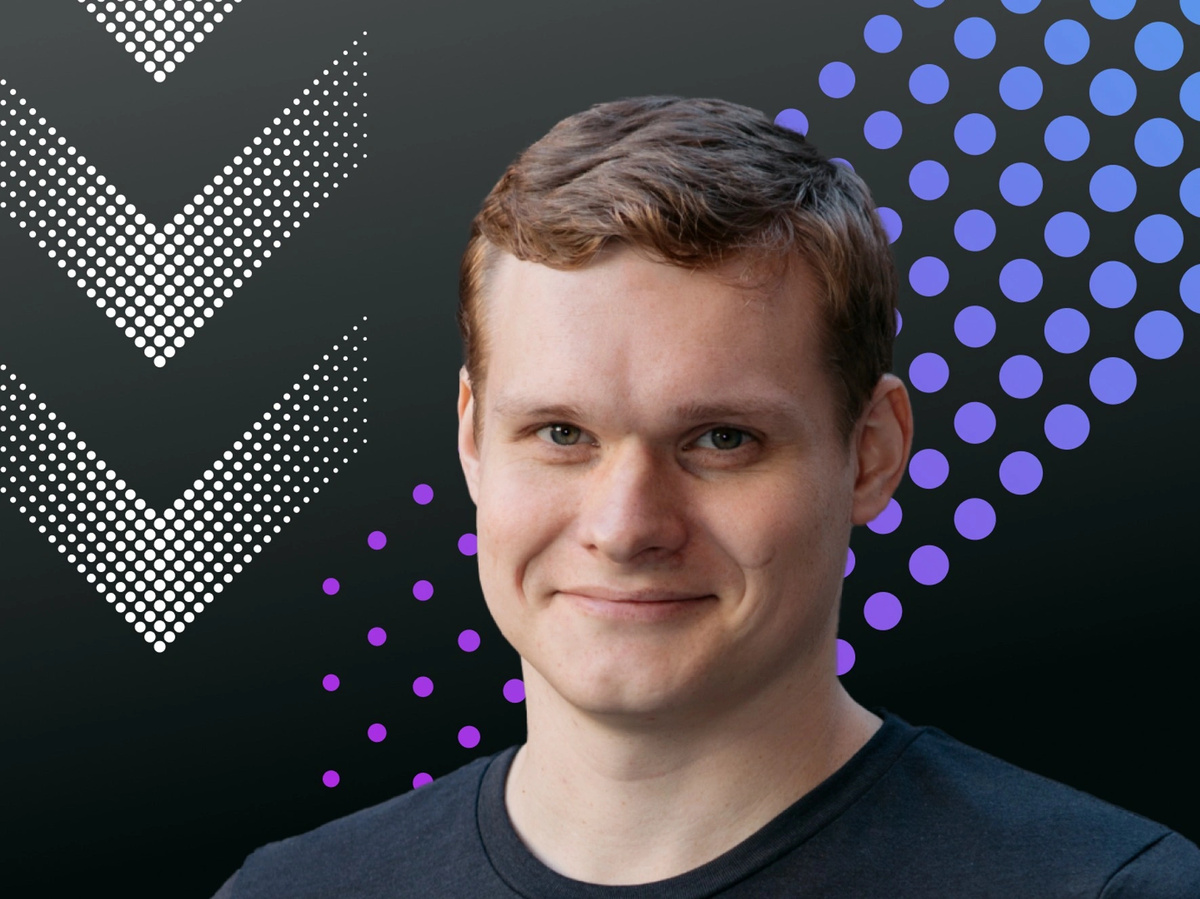
To counter this, Polosukhin advocates for a shift toward AI-driven security auditing and formal verification—a process that uses mathematical proofs to ensure code adheres to strict authorization rules. While NEAR recently demonstrated an AI agent capable of solving complex mathematical benchmarks, the co-founder acknowledges that reliable AI systems are still required to bridge the gap between raw software behavior and formal mathematical models. Beyond automated defenses, he urges developers to abandon traditional API keys in favor of cryptographic authentication, while prioritizing rigorous credential rotation and rapid patching to mitigate immediate exposure.
Comments (0)
No comments yet. Be the first!